STATUSOPEN TO OPPORTUNITIES
Operator Profile · 01

ChandreshKumarKarn. — Cybersecurity Engineer & SOC Leader

CYBERSECURITY ENGINEER × SOC LEADER

SOC Operations · Detection Engineering · SIEM/XDR/SOAR · Incident Response · Security Automation

$whoami →Cybersecurity Engineer

Cybersecurity engineer with 4+ years across SOC operations, SIEM engineering and detection engineering for enterprise clients — log source onboarding and SIEM integration, correlation rule and use case development, detection tuning, incident response and threat investigation.
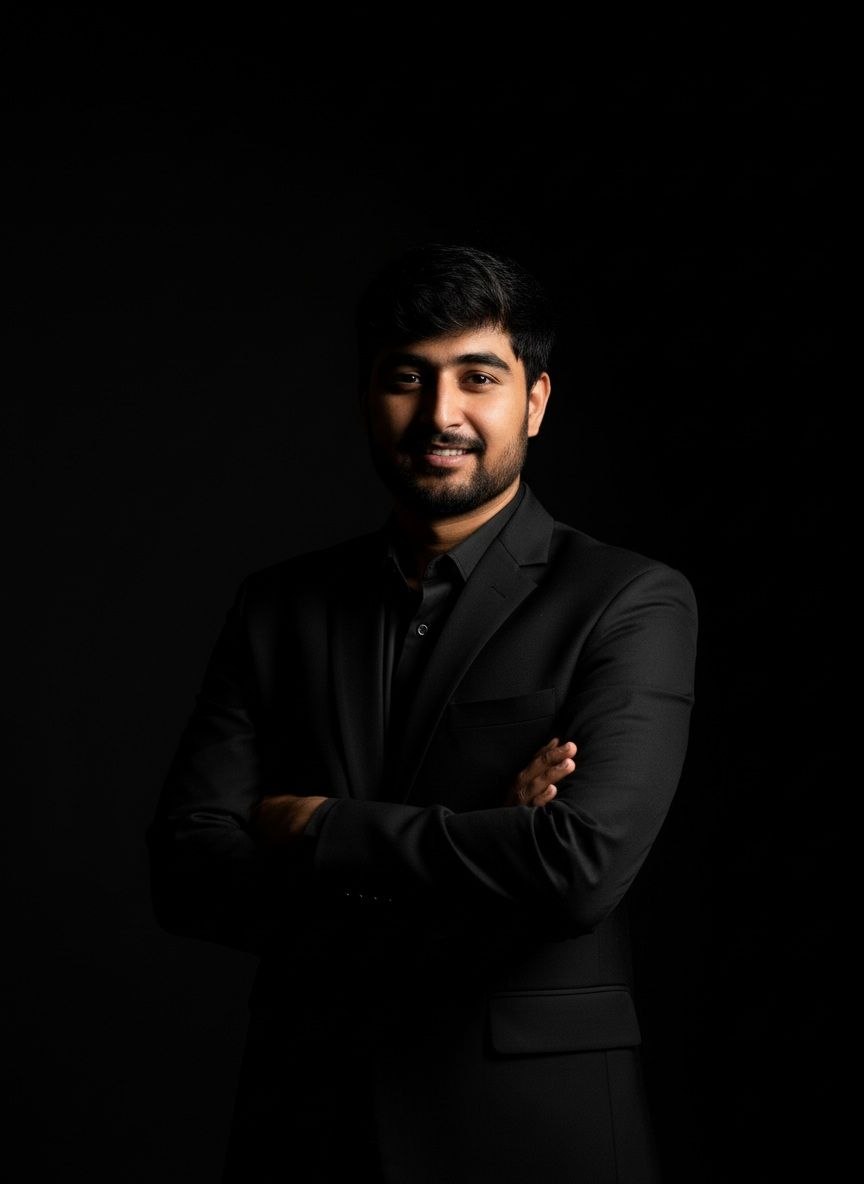
Chandresh Kumar Karn — Cybersecurity Engineer and SOC Leader
ID://SWCK-001 LIVE
01
4+
Years in Cybersecurity
[ALERT] Brute-force attempt blocked · host-redacted[INFO] Correlation rule deployed · detection-content[OK] Response playbook executed · IR workflow[SIM] Synthetic demonstration feed[XQL] Log source health query executed[OK] ATT&CK coverage mapping refreshed
[ALERT] Brute-force attempt blocked · host-redacted[INFO] Correlation rule deployed · detection-content[OK] Response playbook executed · IR workflow[SIM] Synthetic demonstration feed[XQL] Log source health query executed[OK] ATT&CK coverage mapping refreshed

Synthetic telemetry generated for portfolio demonstration. No customer or production data is displayed.

01Professional Summary

The engineer behind SecureWithCK.

SOC operations, incident response, threat hunting, vulnerability management, detection engineering and security automation.

// Dossier
operator.dossier
$ cat /etc/operator
callsignSecureWithCKroleSOC Implementation LeadfocusDetection Eng · SIEM/XDR/SOARlocationIndore, Madhya Pradesh, Indiaopen toBengaluru · Hybrid · Remotestatus● OPEN TO OPPORTUNITIES
▸ mission: onboard the telemetry, engineer the detection, close the incident.
Core Tooling
IBM QRadarQRadar on CloudMicrosoft SentinelSplunkGoogle SecOpsDarktraceCortex XSIAMCortex XDRCortex XSOARMicrosoft DefenderMicrosoft Entra IDActive DirectoryMicrosoft 365 SecurityMicrosoft AzureZscalerCisco IronPortServiceNow
// Narrative

Cybersecurity Engineer with 4+ years of enterprise security experience specializing in SOC operations, incident response, threat hunting, vulnerability management, detection engineering, and security automation. Experienced in SIEM/XDR platforms, enterprise security monitoring, risk-based vulnerability prioritization, security tool integration, and remediation coordination across global client environments. Combining hands-on cybersecurity engineering with an academic foundation in Artificial Intelligence to strengthen threat detection and security operations.

Core Responsibilities
  • 01End-to-end log source onboarding and SIEM integration
  • 02Correlation rule and use case development
  • 03Detection tuning and alert investigation
  • 04Incident triage, response and root cause analysis
  • 05Post-integration and correlation rule validation
  • 06Vulnerability assessment lifecycle and remediation follow-up
  • 07Security posture and SLA reporting
  • 08Junior analyst mentoring and security awareness training
// Capabilities

SOC Operations

Enterprise security monitoring, incident triage and response across US, UK and Singapore client environments.

Detection Engineering

Use case development, correlation rules and detection tuning mapped to MITRE ATT&CK.

SIEM / XDR / SOAR

IBM QRadar, Microsoft Sentinel, Splunk, Darktrace and Cortex XSIAM / XDR / XSOAR.

Log Source Integration

End-to-end onboarding via Syslog, API and agents — parsing, normalization and event categorization.

Incident Response

Triage, forensic analysis, root cause analysis and remediation strategy for escalated incidents.

Security Automation

Automation and tooling with Cortex XSOAR plus Python, PowerShell and Bash.

VAPT & GRC

Independent VAPT engagements, CVSS-aligned risk classification, GRC and data privacy advisory.

Stakeholder Communication

Technical reporting and executive briefings that translate security findings for the business.

02Professional Impact

Evidence, not estimates.

Capability areas backed by hands-on enterprise security operations work. Figures are shown only where they can be stated as fact.

4+
Years in Cybersecurity
End-to-end log source onboarding and SIEM integration
LOG SOURCE ONBOARDING
Correlation rule and use case development, MITRE ATT&CK-aligned
DETECTION ENGINEERING
Incident triage, response, forensic and root cause analysis
INCIDENT RESPONSE
QRadar, Sentinel, Splunk, Darktrace, Cortex XSIAM/XDR/XSOAR
SIEM / XDR / SOAR
Automation and tooling in Python, PowerShell and Bash
SECURITY AUTOMATION
Independent VAPT engagements with CVSS-aligned risk classification
VULNERABILITY ASSESSMENT
GRC advisory and data privacy assessment as a supporting capability
GRC & DATA PRIVACY

Quantified career metrics are deliberately withheld until independently verifiable. Capability statements above describe work performed, not estimated volumes.

03Mission History

Experience timeline.

SOC operations, SIEM integration, detection engineering and incident response for enterprise clients across the US, UK and Singapore — plus independent VAPT, GRC and data privacy consulting.

Jan 2026 — PresentIndore, India

SOC Implementation Lead — Multiple Clients

Tata Consultancy Services Ltd.

Leading end-to-end log source onboarding and SIEM integration across servers, network devices and security tools, through to validated production monitoring readiness.

  • Own end-to-end log source onboarding and SIEM integration for enterprise clients
  • Integrate servers, network devices and security tools via Syslog, API and agent-based collection
  • Build log parsing, normalization and event categorization for onboarded sources
  • Troubleshoot ingestion failures and EPS fluctuations across collection paths
  • Run post-integration validation and correlation rule validation before handover
  • Confirm production monitoring readiness with SOC monitoring teams
  • Coordinate with infrastructure, network and application teams during onboarding
  • Maintain integration documentation to support operational continuity
SIEM IntegrationSyslogAPILog ParsingNormalizationCorrelation Rules
Feb 2024 — Dec 2025Indore, India

SOC Engineer — US & SG Clients

Tata Consultancy Services Ltd.

Enterprise monitoring, incident triage and response, forensic and root cause analysis, vulnerability assessment lifecycle and security posture reporting.

  • Delivered enterprise security monitoring, incident triage and incident response
  • Performed forensic analysis and root cause analysis, then defined remediation strategy
  • Ran the vulnerability assessment lifecycle from discovery through remediation follow-up
  • Produced weekly and monthly security posture and SLA reporting for stakeholders
  • Worked across firewalls, IDS/IPS, DLP and security architecture reviews
  • Delivered security awareness training for client teams
  • Mentored junior analysts on triage quality and escalation discipline
IBM QRadarDarktraceServiceNowIDS/IPSDLPFirewalls
Aug 2022 — Feb 2024Indore, India

SOC Analyst — US & UK Clients (Offsite)

Tata Consultancy Services Ltd.

Monitoring, alert triage and security event analysis with incident investigation and escalation across enterprise client environments.

  • Monitored enterprise environments and triaged security alerts end-to-end
  • Performed security event analysis, incident investigation and escalation
  • Operated IBM QRadar, Darktrace and ServiceNow for detection and case handling
  • Supported forensic analysis and root cause analysis on escalated incidents
  • Contributed to vulnerability assessment activity and remediation follow-up
  • Reviewed firewall, IDS/IPS, DLP and security architecture configurations
  • Authored security documentation, incident response plans and risk assessments
IBM QRadarDarktraceServiceNowIDS/IPSDLPFirewalls
Jan 2024 — Present

Independent Security Consultant — VAPT, GRC & Data Privacy

Self-Employed · Confidential Client (NDA)

Independent VAPT engagements alongside GRC and data privacy advisory, delivered with technical reporting and executive briefing.

  • Delivered independent VAPT engagements; latest assessment covered 3 network segments and 112 assets
  • Performed network and host vulnerability discovery with CVSS-aligned risk classification
  • Identified Critical findings including remote code execution exposure
  • Provided remediation guidance, a technical report, a remediation guide and an executive briefing
  • Added MITRE ATT&CK context and highlighted detection and monitoring blind spots
  • Advised on GRC alignment across ISO 27001, SOC 2, NIST CSF and PCI-DSS
  • Advised on data privacy under GDPR and India's DPDP Act, assessing controls and data-handling practices
VAPTCVSSMITRE ATT&CKISO 27001SOC 2NIST CSFPCI-DSSGDPRDPDP Act
04Capability Hierarchy

Core expertise.

Hands-on experience across security operations, detection, vulnerability management and security engineering.

9 disciplines

Hands-on Experience

SOC Operations (L1/L2)Security MonitoringIncident TriageIncident ResponseIncident ContainmentDigital ForensicsRoot Cause AnalysisSecurity InvestigationThreat HuntingThreat IntelligenceSecurity Operations LeadershipThreat DetectionDetection EngineeringUse Case DevelopmentCorrelation RulesDetection TuningMITRE ATT&CKAlert InvestigationSOC EscalationSLA Management

Hands-on Experience

IBM QRadarQRadar on CloudGoogle SecOpsMicrosoft SentinelSplunkCortex XSIAMCortex XDRCortex XSOARCrowdStrike FalconMicrosoft DefenderDarktrace

Hands-on Experience

Tenable.ioTenable.scVulcan Vulnerability ManagementVulnerability Assessment and Penetration TestingCVSSEPSSCISA KEVRisk-Based Vulnerability PrioritizationExposure ManagementVulnerability RemediationRemediation SLA TrackingRemediation Evidence ValidationExternal Attack Surface ManagementAttack Path Analysis

Hands-on Experience

GitHub Advanced Security (GHAS)Static Application Security Testing (SAST)Dynamic Application Security Testing (DAST)Software Composition Analysis (SCA)Secure Software Development Lifecycle (SSDLC)CI/CD SecurityMicrosoft AzureMicrosoft Azure SecurityWindows SecurityLinux SecurityContainer and AKS Security Fundamentals

Hands-on Experience

PythonPowerShellBashSQL/MySQLXQLAQLKQLLog Source OnboardingLog Source IntegrationSIEM IntegrationSecurity Tool IntegrationSyslogAPI IntegrationAPI AutomationAgent-Based CollectionLog ParsingNormalizationEvent CategorizationSecurity AutomationSecurity Dashboards and ReportingPower BIExcel

Hands-on Experience

ServiceNowServiceNow CMDBJiraAsset Inventory and ReconciliationSecurity Monitoring Coverage AnalysisGRC AdvisoryISO 27001NIST CSFSOC 2PCI-DSSGDPRIndia's DPDP ActControls & Policy AssessmentRisk Assessment

Hands-on Experience

AI-Assisted Threat DetectionAI-Enabled Ransomware AwarenessAI-Assisted Vulnerability DiscoveryAI Threat ModellingAgentic AI Security AwarenessThreat-Led Security Testing

Hands-on Experience

Microsoft Entra IDActive DirectoryMicrosoft 365 SecurityZscalerCisco IronPortIDS/IPSDLPFirewalls

Hands-on Experience

VAPT MethodologyITIL-aligned Incident ResponseSecurity Architecture
05Security Engineering Portfolio

Built, not just operated.

Security tooling engineered hands-on — led by the Secure - One XDR engineering project.

FLAGSHIP PROJECT

Secure - One

From SOC Operations to Security Product Engineering

Secure - One is an independently engineered XDR project focused on Windows endpoint telemetry, threat detection, behavioral analysis, threat intelligence, and coordinated security response.

Extended Detection and Response (XDR)GoWindows Endpoint SecurityDetection EngineeringSigma RulesBehavioral DetectionThreat IntelligenceHost FirewallIncident ResponseSOC Engineering
$ secure-one --pipeline
  1. 01Windows Endpoint
  2. 02Go Endpoint Agent
  3. 03Telemetry Collection
  4. 04Event Normalization
  5. 05Detection Engine
  6. 06Alert Processing
  7. 07Management Backend
  8. 08XDR Console
Threat Intelligence Utility

Bulk IP/URL/Domain Reputation Checker

Python-based threat-intelligence reputation utility for batch IP, URL and domain lookups supporting SOC triage.

PythonThreat Intel APIs
Log Analysis

LogSense

Security log analysis utility that parses security event data and surfaces anomalies to speed investigation and detection workflows.

PythonLog ParsingDetection Logic
Posture Scanning

Domain Security Checker

Automated domain-security posture scanner covering DNS, SSL/TLS and related configuration checks.

PythonDNSSSL/TLS
Platform Concept

Threat Intelligence Platform

Centralized platform concept for aggregating and correlating threat-intelligence feeds to support proactive detection and use case development.

Threat Intel FeedsCorrelation
// Additional Technical Projects
AI Virtual Painter · PatentedReal-Time Face Mask Detection System · Computer visionSmart Blind Stick & Glasses · Assistive hardware
06Real cybersecurity problems. Sanitized. Explained.

Case files.

Selected technical investigations, engineering challenges and SOC improvements presented without exposing customer-confidential information.

All case studies are sanitized. Customer names, infrastructure identifiers, IP addresses, internal configurations and confidential information have been removed or generalized.

07Interactive SOC Lab · Simulation

SOC monitoring, demonstrated.

A simulated security operations view built to demonstrate detection engineering, ATT&CK coverage mapping and triage workflow — using synthetic data only.

SIMULATED ENVIRONMENT · Synthetic telemetry generated for portfolio demonstration. No customer or production data is displayed.

+4
27
Active Alerts
-2
8
Incidents (24h)
+12
342
Detections Online
+0.3
4.6/5
Maturity Score
GLOBAL THREAT MAP
LIVE · UTC
THREAT FEED
● CRITICAL00:12
Lateral movement detected · host-WIN-44
● HIGH00:34
Credential dumping (T1003.001) · DC-EAST
● MED01:02
DNS tunneling pattern · 10.0.4.18
● LOW01:18
Unusual login geo · user.svc
● HIGH01:44
Suspicious PowerShell exec (T1059.001)
MITRE ATT&CK COVERAGE
simulated coverage map
TA1001
Initial Access
TA1002
Execution
TA1003
Persistence
TA1004
Priv Escalation
TA1005
Defense Evasion
TA1006
Credential Access
TA1007
Discovery
TA1008
Lateral Movement
TA1009
Collection
TA1010
C2
TA1011
Exfiltration
TA1012
Impact
08Supporting Differentiator

GRC & data privacy.

An extension of hands-on cybersecurity engineering — not the primary career identity. No compliance scores or maturity percentages are claimed.

GRC Advisory

Controls and policy assessment against ISO 27001, SOC 2, NIST CSF and PCI-DSS, carried out alongside hands-on security operations work.

Data Privacy

Data privacy advisory under GDPR and India's DPDP Act — reviewing data-handling practices and the controls that support them.

Risk Assessment

Risk assessment and CVSS-aligned classification of findings, with remediation guidance mapped to business impact.

Executive Reporting

Technical reports, remediation guides and executive briefings that translate security findings for non-technical stakeholders.

// Frameworks & Regulations Worked With
GRC AdvisoryISO 27001SOC 2NIST CSFPCI-DSSGDPRIndia's DPDP ActControls & Policy AssessmentRisk AssessmentData-Handling Practice AssessmentExecutive Reporting
09Credentials

Certification, training & education.

Only credentials that are actually held. Training and courses are labelled as such, never presented as certifications.

Certification / Credential
  • Microsoft Azure Certification
    TCS / Microsoft
Professional Training & Courses
  • Software Security AssuranceTCS HiTech
  • Unix/Linux BasicsRedHat
  • Data Science SpecializationUniversity of Michigan (Coursera)
  • Applied Machine Learning in PythonUniversity of Michigan (Coursera)
  • R ProgrammingJohns Hopkins University (Coursera)
  • Introduction to Machine LearningDuke University (Coursera)
  • Business CommunicationTCS
  • Machine First and Intelligent Business ProcessesTCS
Education
B.Tech, Artificial Intelligence
Sage University, Indore
2018 — 2022 · 90% Aggregate
10Recognition

Achievements & recognition.

Verified recognition only — awards, speaking invitations and academic honours as stated on the resume.

Most Influential Data Analytics Professional – Asia Pacific

EIILM Kolkata & CMO Asia · Sep 2024

Invited guest speaker and panelist for contributions to data analytics.

Golden Guru 2023

Tata Consultancy Services · 2023

Recognized for voluntarily training unallocated TCS associates in Python and Machine Learning.

Xperience Learner

Tata Consultancy Services · Nov 2022

Completed advanced technical courses and ranked among top performers company-wide.

Sage Career Day 2025

Sage University, Indore · 2025

Recognized as Best Student of the 2018–2022 term for academic and cybersecurity performance.

1st Rank — Research Paper Writing Competition

Micro Focus International plc · 2020

Paper: Classification of Shoppers' Intention.

THOUGHT LEADERSHIP

Signal, not Noise

Cybersecurity education and field notes from SOC operations. Published items link to the source; everything else is marked upcoming.

#30DaysSOCSeries

PUBLISHED ON LINKEDIN

A practical cybersecurity series covering SOC operations, alert triage, security monitoring, cybersecurity labs, career development, and defensive security concepts.

Practical lessons and perspectives on SOC operations, defensive security, hands-on learning, and building a career in cybersecurity.

CK
Chandresh Kumar Karn
Cybersecurity Engineer · SOC Leader
#SecureWithCK

Engineering detections that don't drown analysts

How I score detection logic for fidelity, context and analyst actionability before it goes live in production.

COMING SOON
CK
Chandresh Kumar Karn
Cybersecurity Engineer · SOC Leader
#SecureWithCK

QRadar → Cortex XSIAM: migrating without coverage gaps

Detection parity, log source onboarding order and cutover sequencing — notes from real platform migration work.

COMING SOON
CK
Chandresh Kumar Karn
Cybersecurity Engineer · SOC Leader
#SecureWithCK

Where automation actually helps a SOC

Practical SOAR and enrichment patterns that reduce analyst toil, and the ones that only add moving parts.

COMING SOON
12Availability

Open to opportunities.

Looking for roles centred on SOC engineering, detection engineering, SIEM/XDR/SOAR, incident response and security automation — with VAPT, GRC and data privacy as secondary areas of fit.

Cybersecurity Engineer
Security engineering across detection, monitoring and automation
SOC Engineer / Senior SOC Analyst
Monitoring, triage, investigation and escalation ownership
SOC Implementation Engineer / Lead
Log source onboarding, SIEM integration, production readiness
Detection Engineer
Use cases, correlation rules, tuning, MITRE ATT&CK coverage
SIEM / XSIAM / XDR Engineer
Cortex XSIAM/XDR, IBM QRadar, Microsoft Sentinel, Splunk
SOAR / Security Automation Engineer
Cortex XSOAR playbooks, Python / PowerShell / Bash automation
Incident Response Engineer
Triage, containment, forensic and root cause analysis
Security Operations Engineer
Tooling, pipelines, log source health, operational continuity
Cyber Defense Analyst
Threat detection, hunting and security event analysis
Cybersecurity Consultant
Advisory across security operations and detection maturity
$ status --hiring
Open to cybersecurity opportunities
Indore, India · Open to Bengaluru / Hybrid / Remote
13For Recruiters & Hiring Managers

Let’s talk about the role.

Recruiters, hiring managers and security leaders — reach out about cybersecurity engineering, detection engineering, SIEM/XDR or SOC leadership opportunities. I respond to every genuine enquiry.

hiring@securewithck:~$